ALT-001 High Malicious True Positive
Mimikatz credential theft tool
16 Aug 2026 ec2amaz-9oh9aqq / NT AUTHORITY\SYSTEM
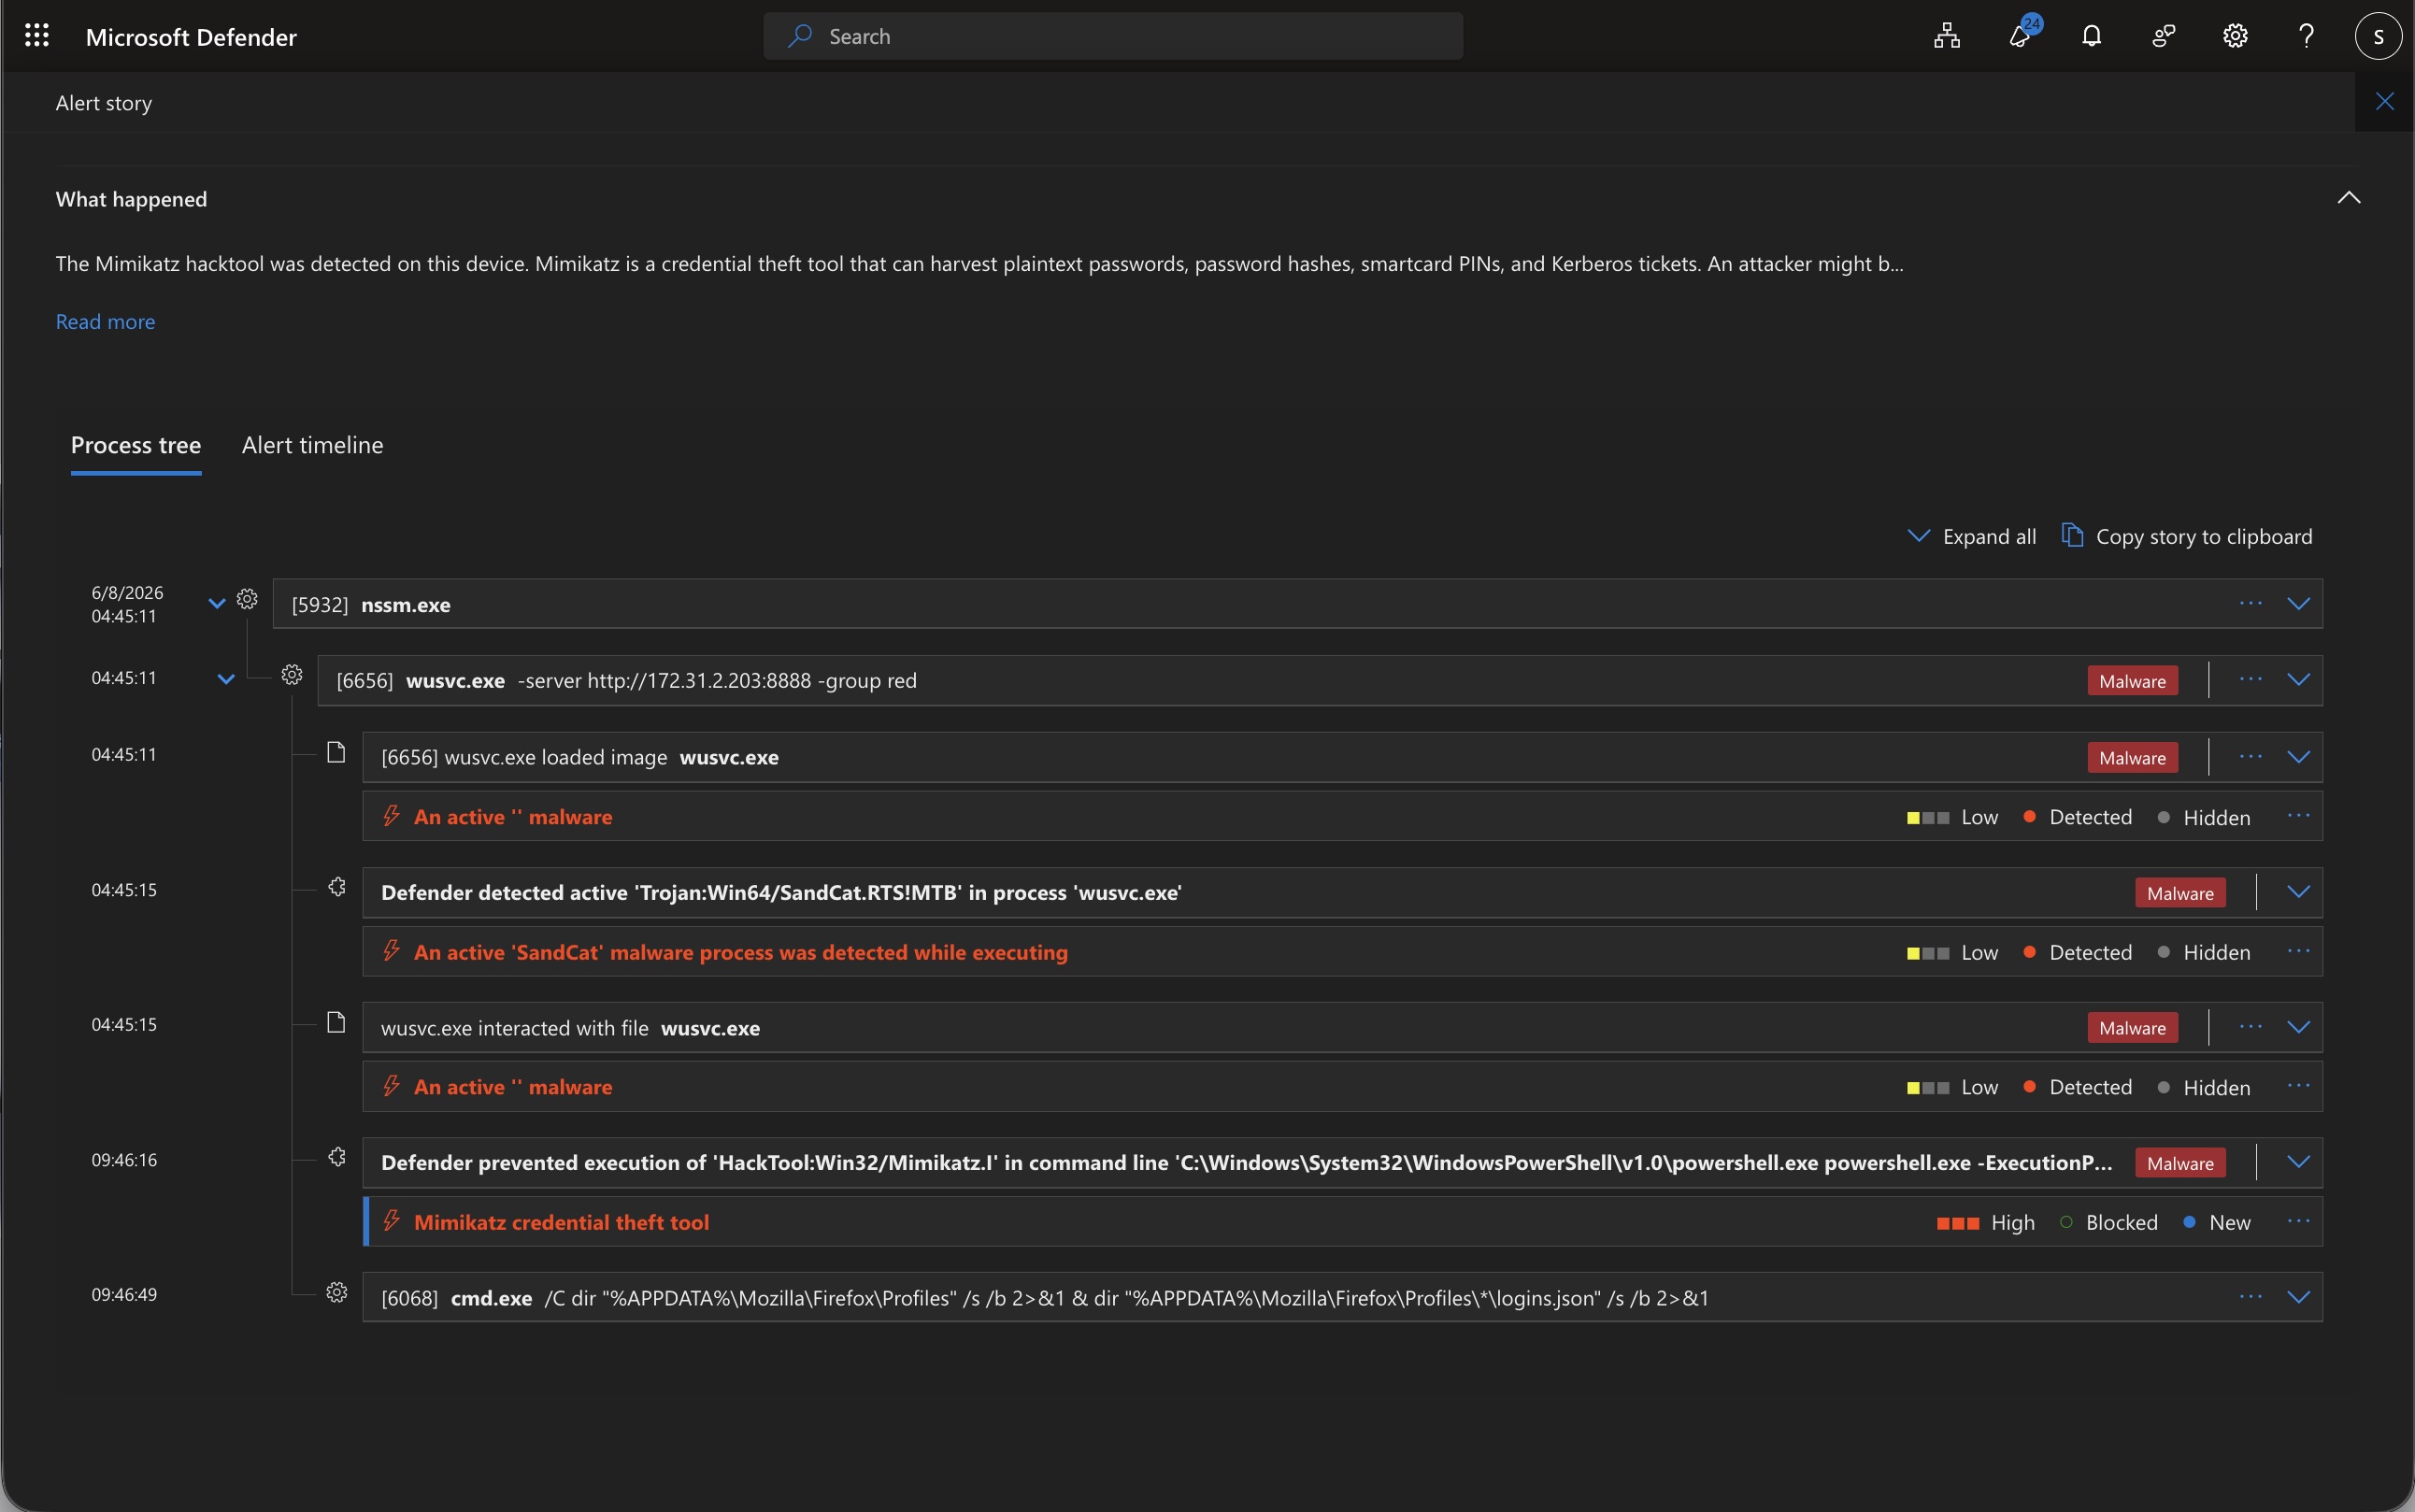
A suspicious wusvc.exe process associated with a Sandcat/CALDERA agent was running on the endpoint.
The process executed PowerShell commands that downloaded and attempted to execute Mimikatz, a credential access tool.
The Mimikatz command included,
- privilege::debug - Attempts to enable the Windows debug privilege, which allows Mimikatz to access protected processes such as LSASS.
- sekurlsa::logonpasswords - Attempts to extract credential information from Windows authentication processes.
- Microsoft Defender detected and blocked the Mimikatz execution attempt.
- Additional command activity showed the system searching for Firefox profile locations and logins.json files, indicating an attempt to locate stored browser credential data.
Completed in a
live SOCSIM lab
live SOCSIM lab